Healthcare software has to do two things at once: feel simple for patients and clinicians, and protect sensitive health information to a standard regulators, hospitals and health plans will accept. Get the first wrong and nobody uses it. Get the second wrong and it cannot be sold.
Kreatorz builds healthcare apps with both in mind. We are a US company with an office in Sheridan, Wyoming, and a team on Eastern Time in Brantford, Ontario. Our designers, engineers and cloud specialists build HIPAA safeguards into the architecture from the first sprint, rather than bolting them on before launch.
Healthcare apps we build
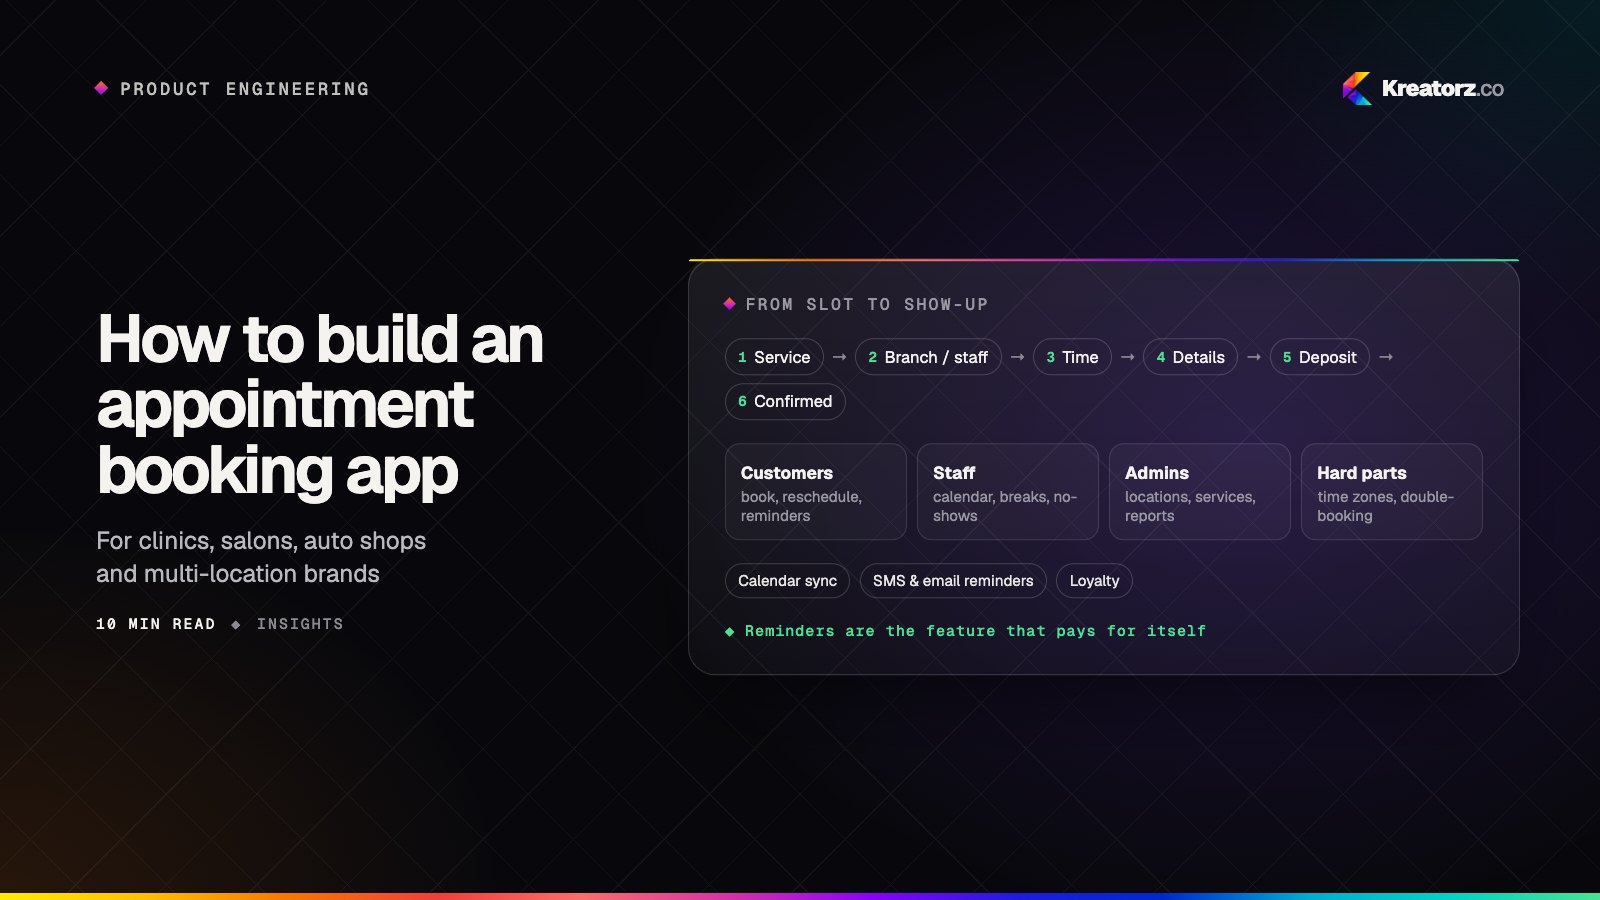
- Patient apps — appointment booking, reminders, records and results, secure messaging, payments and follow-up care.
- Telemedicine and telehealth platforms — video visits, scheduling, intake forms, e-consent, visit notes and secure chat for providers and patients.
- Remote patient monitoring — apps that connect to wearables and connected devices, with dashboards and alerts for care teams.
- Provider and practice tools — scheduling, intake, care coordination and reporting for clinics, practices and multi-location groups.
- Wellness and digital health products — consumer health, fitness and mental-wellbeing apps, designed with privacy as a feature.
- AI in healthcare — note summarization, patient question answering grounded in approved content, and triage support, always with clinicians in the loop. See AI app development.
Examples of our work
- Rose Optometry — a patient-first platform that brings eyewear browsing, eye exam booking and follow-up care together in one experience.
- Luna — an AI-powered pet health app that answers questions around the clock and analyzes symptoms and photos.
HIPAA compliance built in, not bolted on
If your product handles protected health information for a hospital, clinic, practice or health plan, HIPAA applies. We design for it from discovery onward:
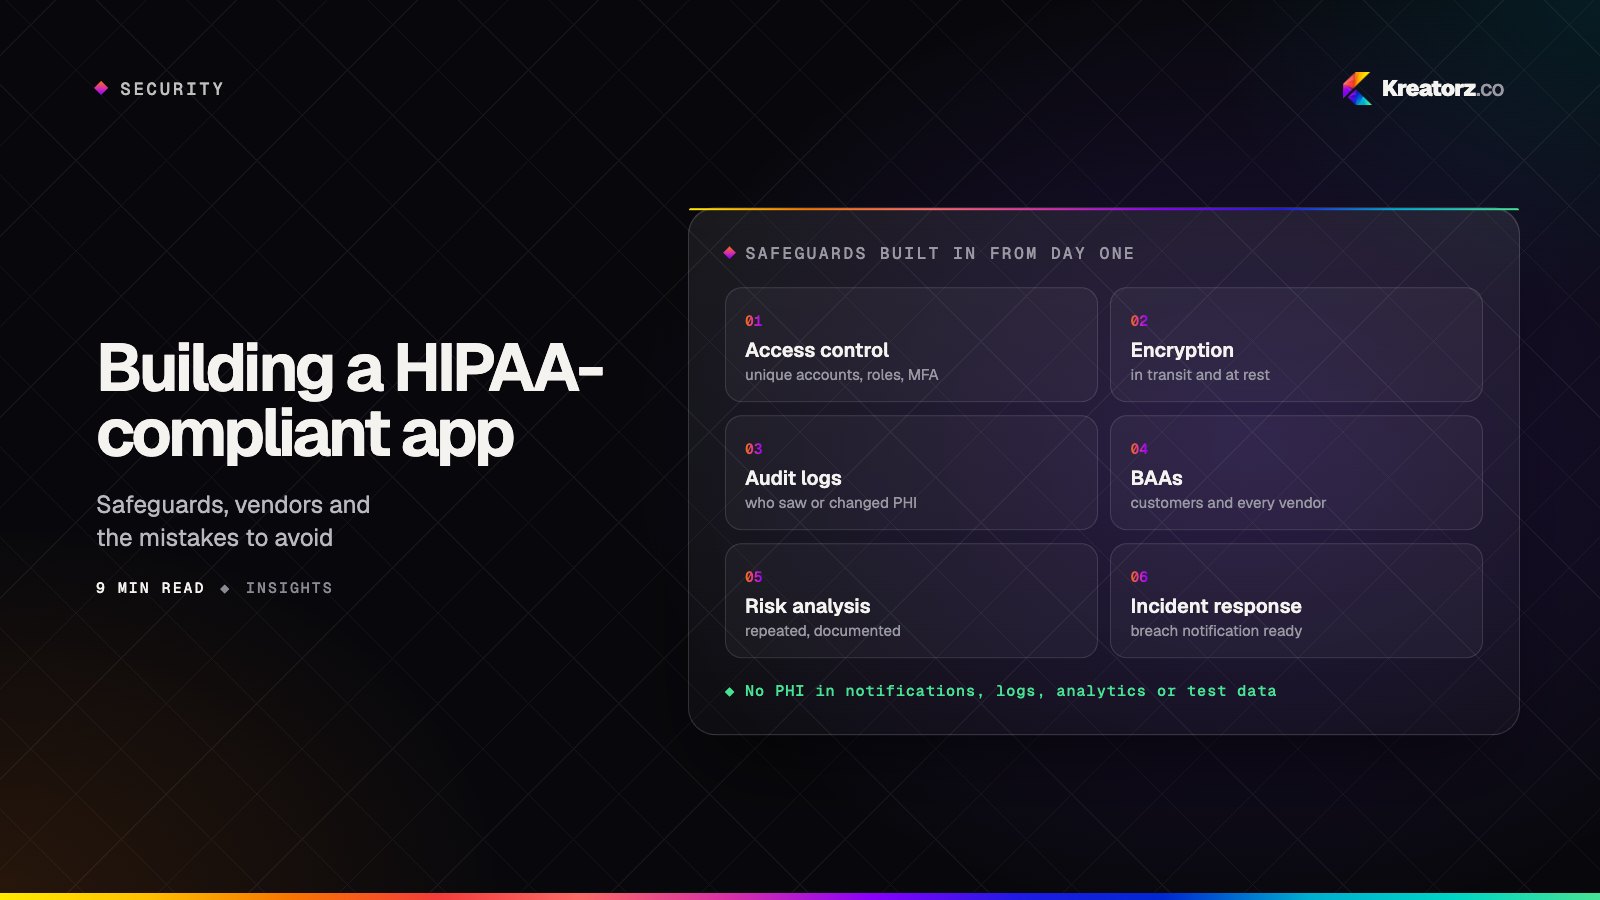
| Safeguard | What we build |
|---|---|
| Access control | Unique accounts, role-based permissions, multi-factor authentication and session timeouts |
| Encryption | TLS for every connection, encryption at rest for databases, files and backups with managed keys |
| Audit controls | Tamper-resistant logs of who viewed or changed health information, and when |
| Vendors and BAAs | PHI kept only in services covered by business associate agreements, such as HIPAA-eligible AWS services |
| Safe defaults | No PHI in push notifications, logs, analytics or test environments |
| Resilience | Tested backups, disaster recovery and monitoring |
HIPAA compliance is an ongoing program that belongs to your organization, so we work alongside your compliance and legal advisors, and we provide the technical safeguards and documentation they need. Our guide to building a HIPAA-compliant app explains the rules, the business associate agreements and the most common mistakes in detail.
Integrations
Healthcare apps rarely stand alone. We integrate with EHR and practice-management systems through their available APIs (including FHIR-based APIs where offered), payment providers, video-calling services, e-prescribing and lab partners, and wearable platforms such as Apple HealthKit and Google Health Connect.
How we work
- Discovery — users, workflows, data flows and compliance requirements, ending with a scoped plan and estimate.
- Design — accessible, calm interfaces tested with patients and clinicians.
- Build — working software every one to two weeks with security reviews built into each cycle.
- Validate — security testing, accessibility checks and a pilot with real users.
- Launch — app store submission, monitoring and support. See our guide to launching on the App Store and Google Play.
Start your healthcare project
Tell us who your product serves and what it needs to do. We will help you scope a first release with compliance designed in. Get a free consultation.